Blog & Insights
Expert perspectives on cybersecurity, compliance, and IT strategy.
OT and IT still flat: how construction and plant networks get carved without stopping jobs
If a guest laptop or office PC can reach PLC, CNC, or site controllers, you do not have OT. You have a flat network with machines on it. Here is how construction and manufacturing teams carve it without taking production offline.
Read more
Shadow AI on the shop floor: a practical AI policy for manufacturers
Your people are already pasting quotes, drawings, and supplier emails into AI tools. Banning it does not work and ignoring it is worse. Here is a practical AI policy manufacturers and DoD suppliers can roll out in 30 days.
Read more
Fake bank change, real money gone: stopping payment fraud in construction
One email from a sub with new banking details, one updated vendor record, and a pay app goes to a fraudster. Here is how business email compromise hits contractors and the simple controls that stop it.
Read more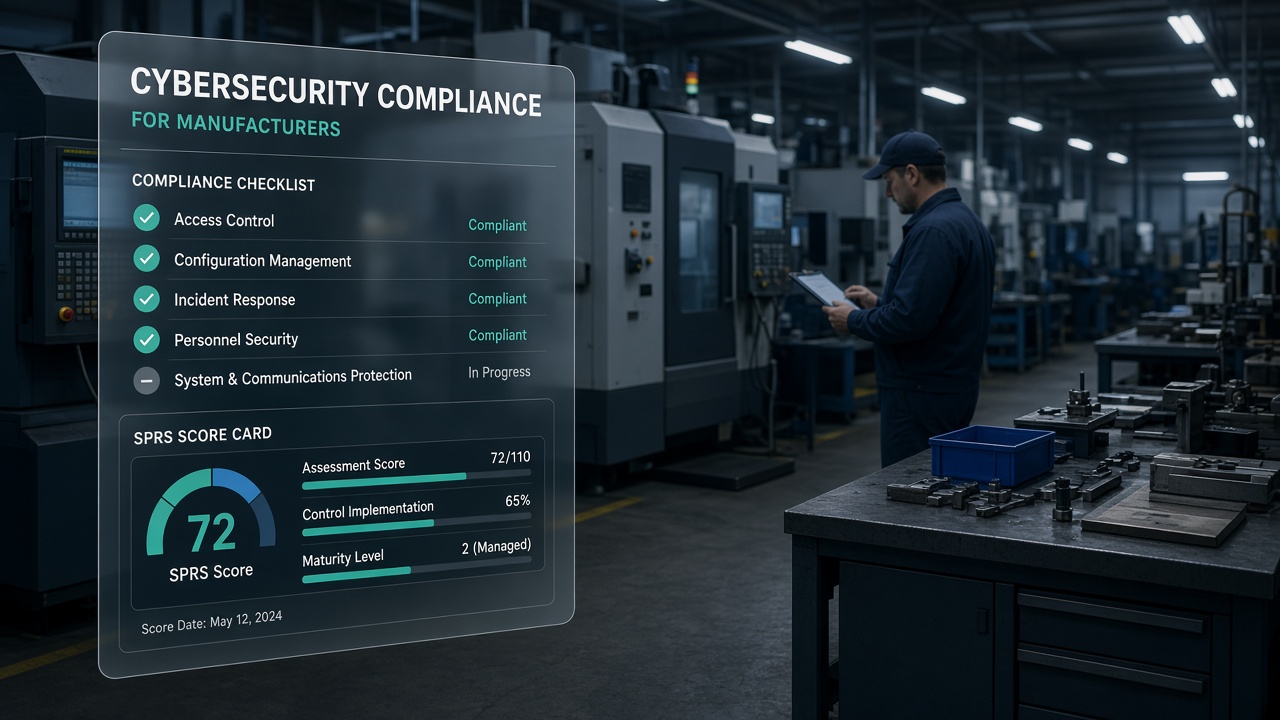
When CMMC Phase 2 is paused, what manufacturers should still do on NIST 800-171 and SPRS
CMMC Phase 2 third-party assessments are on hold. DFARS 7012, NIST 800-171, and honest SPRS scores are not. Here is what manufacturers and DoD suppliers should keep doing while the timeline is uncertain.
Read more
Choosing the Right Cybersecurity Firm: 2026 Buying Guide and Provider Directory
A transparent, segment-aware guide to evaluating cybersecurity companies in 2026 — software vendors, endpoint specialists, and operational MSSPs compared.
Read more
The Rise of AI-Powered Phishing Attacks in 2026
As AI-powered phishing attacks become increasingly sophisticated, businesses must understand the new threat landscape. This article explores how attackers use generative AI to create hyper-personalized campaigns and provides actionable defense strategies.
Read more
Ransomware-as-a-Service: Why SMBs Are the New Target
Mid-market businesses face a growing threat from Ransomware-as-a-Service (RaaS) attacks. Understand the RaaS model and learn which essential security controls can effectively mitigate your risk and reduce impact.
Read more
Zero Trust Architecture: A Practical Roadmap for 2026
This article provides a practical, step-by-step roadmap for mid-market businesses to implement a Zero Trust security model by 2026 without a complete overhaul of their existing technology stack.
Read more
Supply Chain Attacks: Lessons from Recent Software Breaches
Third-party software compromises, like the SolarWinds breach, pose a significant threat. Learn how these supply chain attacks happen and how to effectively evaluate vendor risk to protect your organization.
Read more
CMMC 2.0 Compliance: What Defense Contractors Must Do Now
The Department of Defense's CMMC 2.0 mandate is here, and the timeline for compliance is shrinking. This article provides practical guidance for defense contractors on preparing for certification, identifying common gaps, and understanding timeline expectations.
Read more
Deepfake Fraud in the Boardroom: The New CEO Scam
Deepfake technology is the new frontier of CEO fraud, enabling criminals to impersonate executives with alarming accuracy. Learn how to spot these synthetic voice and video scams and protect your business from this emerging threat.
Read more
Cloud Misconfigurations: The #1 Cause of Data Breaches
Cloud misconfigurations are the leading cause of data breaches, not complex hacks. Learn the most common AWS, Azure, and M365 security gaps and the practical steps to detect, remediate, and secure your business-critical data.
Read moreExplore TRNSFRM
Take the next step beyond the blog.
Case Studies
Real CMMC, NIST, and FTC outcomes from clients.
Free Compliance Checklist
Score yourself across 47 controls in 10 minutes.
Compliance Frameworks
CMMC, NIST 800-171, ISO 27001, HIPAA, FTC, ITAR.
Industries We Serve
Manufacturing, construction, automotive, healthcare.
Managed IT Services
Help desk, infrastructure, and proactive monitoring.
IT Resilience Framework
Assess, Remediate, Operate, Improve. A continuous lifecycle.